Security Incident at Third-Party Email Provider Brevo Impacts Crypto Users
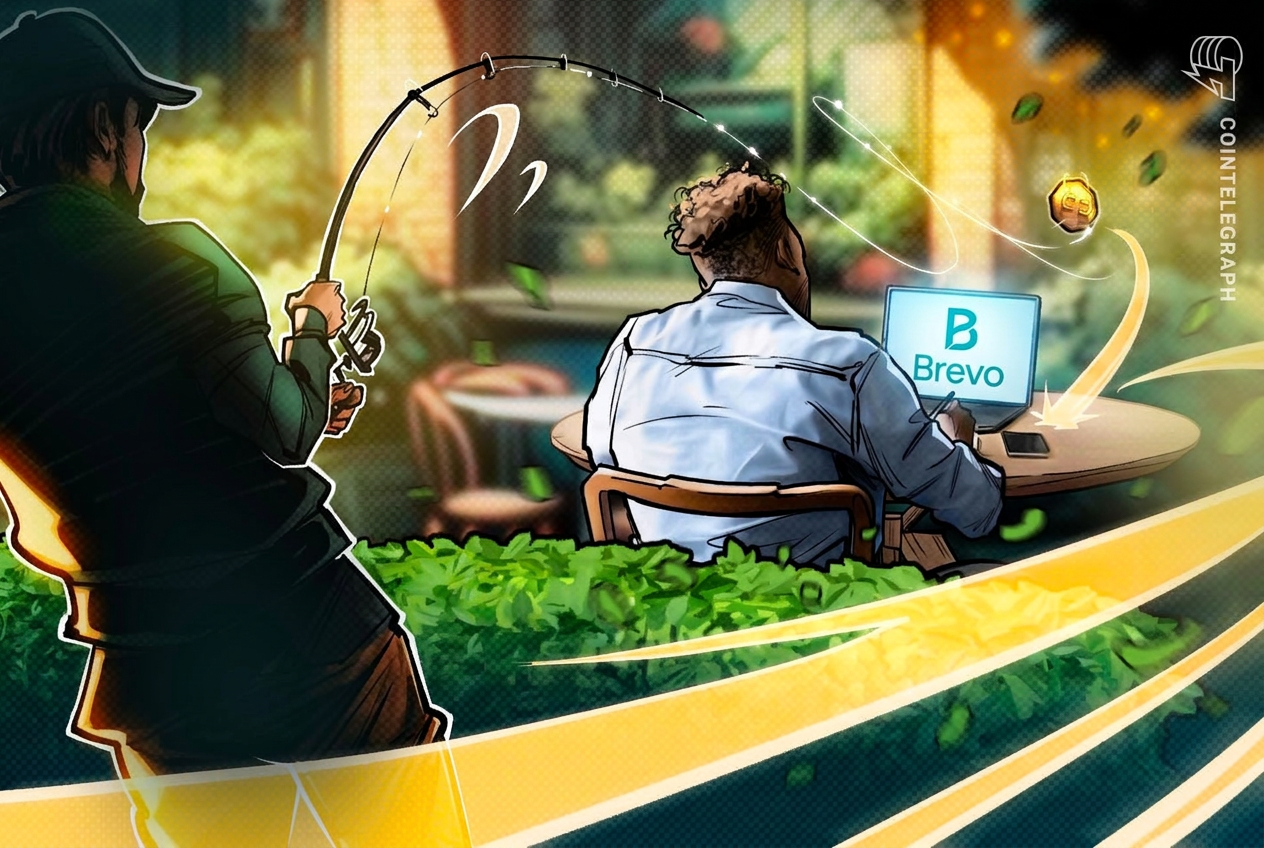
A significant security flaw at the email marketing and newsletter platform Brevo has resulted in a widespread phishing campaign targeting 347,000 subscribers of cryptocurrency hardware wallet manufacturer Trezor. The incident highlights the persistent risks crypto companies face when relying on external service providers for customer communications.
According to official statements from Trezor, an unauthorized party gained access to Brevo’s systems through a login vulnerability. The attackers subsequently utilized the compromise to dispatch unauthorized, malicious emails to a database of Trezor newsletter subscribers. In response to the breach, Trezor confirmed that it is treating every exposed email address as compromised and potentially subject to follow-up social engineering attempts.
The Mechanics of the Attack
Phishing campaigns aimed at cryptocurrency investors often leverage urgency and fear to deceive users into taking immediate action. In this specific breach, the attackers utilized Brevo’s legitimate email infrastructure to send messages that appeared genuine, bypassing many standard email spam filters that rely on domain verification mechanisms like SPF and DKIM.
Because the emails originated directly from a compromised account within a trusted marketing platform, recipients received communications containing authentic branding. The malicious messages typically contained links directing users to fraudulent web pages designed to harvest sensitive credentials, seed phrases, or private keys.
Trezor swiftly issued alerts to its user base, reiterating that hardware wallet security remains intact at the device level, but urging extreme caution regarding digital communications. The company stressed that it will never request a user’s recovery seed phrase under any circumstances.
Supply Chain Risks in the Cryptocurrency Ecosystem
This incident is not an isolated event in the Web3 space. Third-party marketing software, customer support software, and email delivery platforms have repeatedly emerged as prime targets for cybercriminals seeking entry into the digital asset industry. Because top-tier cryptocurrency companies maintain robust security around their core blockchain applications and cold storage solutions, malicious actors frequently target third-party vendors as soft entry points.
Similar breaches involving marketing platforms like Mailchimp and customer service management tools have previously resulted in leaked email lists and targeted phishing campaigns across multiple crypto platforms. The incident underscores a growing security challenge: even when a hardware wallet manufacturer maintains flawless cryptographic security on its physical devices, vendor management remains a vulnerable vector.
- Third-party reliance: External vendors often store sensitive contact lists that become valuable targets for attackers.
- Domain reputation abuse: Using compromise-driven access to legitimate email services allows attackers to pass automated authentication checks.
- Data aggregation: Cybercriminals cross-reference stolen email databases from multiple breaches to refine their targets.
Why Hardware Wallet Users Are Targeted
Hardware wallets like Trezor and BitBox store private keys in isolated offline hardware environments, protecting funds from remote software malware and network exploits. Because attackers cannot extract private keys directly from a secure hardware element remotely, social engineering becomes their primary weapon.
Phishing campaigns attempt to trick wallet owners into manually typing their 12- or 24-word recovery seeds into fraudulent websites, fake firmware update tools, or spoofed desktop applications. Once an attacker obtains the recovery seed, they can instantly recreate the wallet on their own device and drain the associated digital assets, bypassing all hardware protections entirely.
Essential Security Measures for Digital Asset Holders
In light of the Brevo security incident and the ongoing threat of sophisticated social engineering attacks, digital asset holders must exercise heightened vigilance when interacting with online communications.
- Protect Your Recovery Seed: Never type your recovery seed words into any computer, smartphone, website, or form. Recovery seeds should only ever be entered directly into the physical hardware wallet device itself during recovery procedures.
- Treat Unsolicited Emails with Suspicion: Assume any email requesting urgent account verification, firmware upgrades, or emergency action is fraudulent, regardless of how official the sender address appears.
- Use Unique Email Addresses: Consider using dedicated alias email addresses for crypto-related services and hardware wallet newsletters to prevent primary email addresses from being linked to crypto holdings.
- Bookmark Official Websites: Access wallet management platforms, software downloads, and firmware updates exclusively through verified, bookmarked web addresses rather than clicking links embedded within emails.
- Verify Firmware via Official Software: Genuine firmware updates for hardware wallets are always managed natively through official desktop clients, such as Trezor Suite, rather than third-party web links.
Conclusion
The breach involving Brevo and Trezor serves as a stark reminder of the complexities surrounding cybersecurity in the digital asset domain. While cold storage hardware remains one of the safest methods for securing cryptocurrencies, human vigilance remains the final line of defense against supply chain breaches and deceptive phishing operations. As cybercriminals continue to exploit third-party vulnerabilities, cryptocurrency users must maintain a strict posture of zero trust toward all incoming digital communications.